Sensitive data is classified where it is produced, and stopped there.
Verifyi recognises personal data, financial data and source code in place: on Windows and Linux endpoints, inside TLS traffic and in cloud stores. Policy is enforced on the endpoint; only the verdict reaches the console. Everything runs in your own data centre, installed from two ISOs.
Every path data can take out is covered by the same rule set
Endpoint DLP
Clipboard, file movement, USB and shadow copy, printing, mobile devices, browser; a single agent written in Rust for Windows and Linux.
Network DLP
A proxy appliance that inspects TLS with its own CA; agent-based or Active Directory (Kerberos) identity mode; web categories and generative-AI platform packs.
Discovery and classification
Data-at-rest scans across endpoints, databases, SharePoint/OneDrive and object stores; KVKK, PCI-DSS and HIPAA scan profiles; MIP sensitivity labels.
CASB and extensions
Secret and personal-data scanning in GitHub repositories; a Chromium extension for DLP in generative-AI prompts; an Office add-in for labelling.
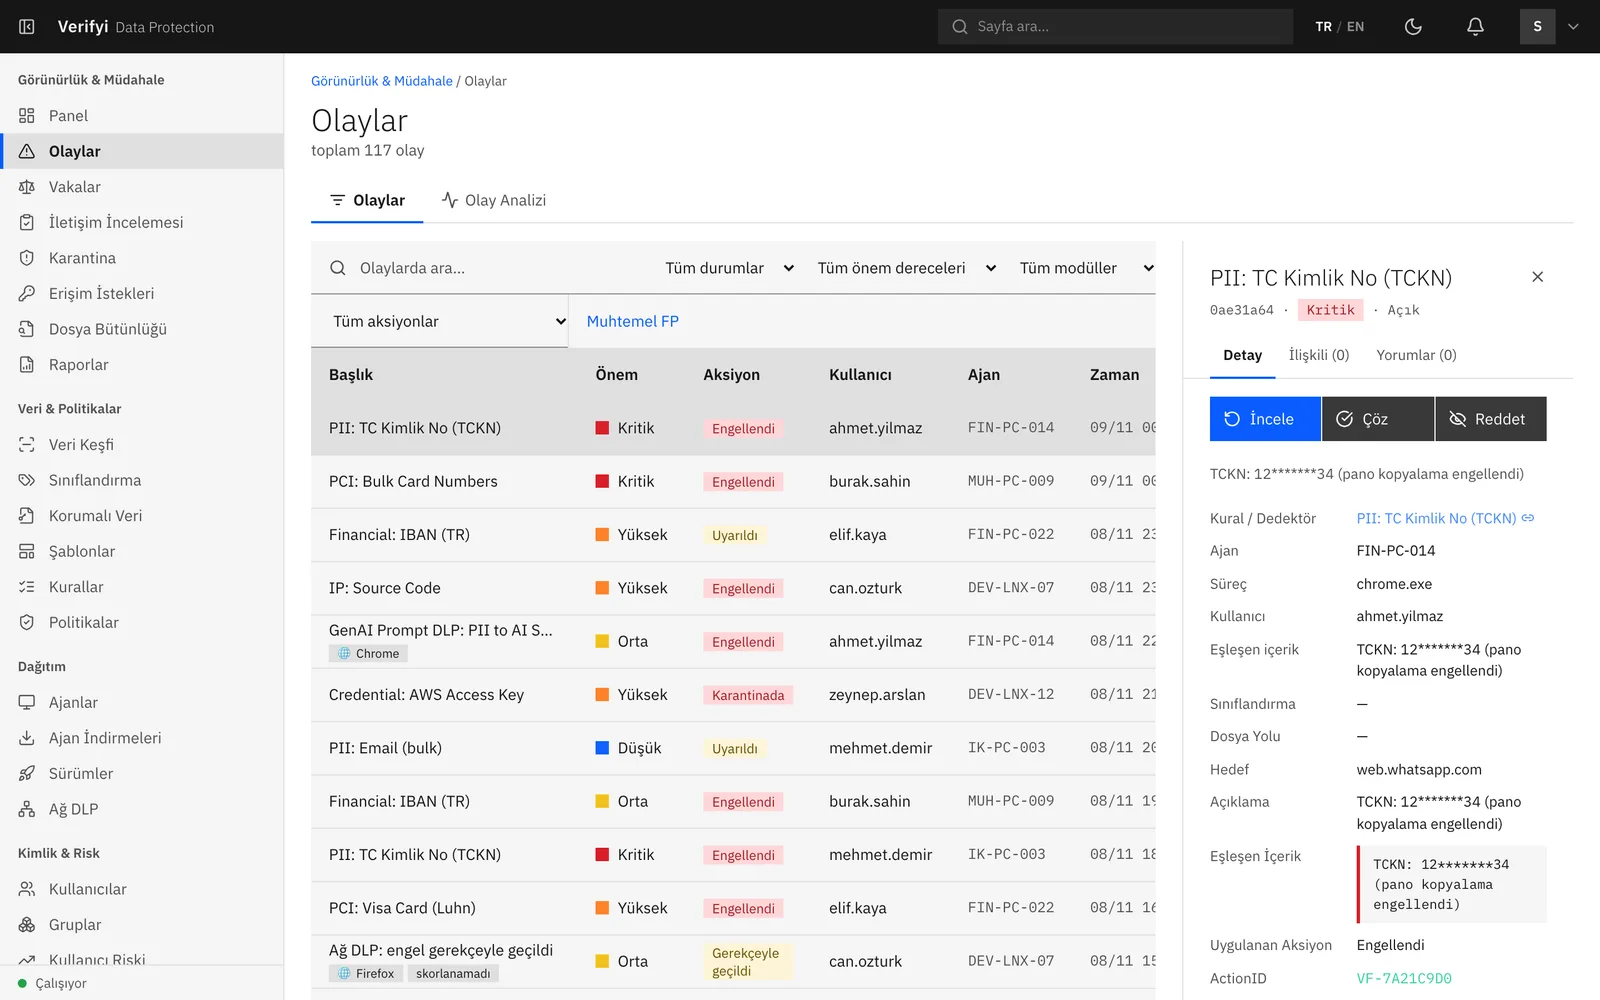
Every incident: who, which device, which rule, which destination
Incident list and detail panel on one screen; the matched content arrives masked, the applied action and justification are recorded. The interface is bilingual.
Five tiers, asynchronous, one decision
Every file and every request goes through the same sequence. Cheap tiers decide early; expensive tiers run only when needed. That is how the agent stays inside its two-percent CPU target.
- 01
Metadata
Extension, size, MIME type, owner, encrypted Office/PDF detection. An encrypted file is never treated as clean; it is reported as its own event type.
- 02
Regex and validation
Turkish national ID (TCKN), IBAN, card numbers (Luhn), e-mail, phone; context windows and distinct-value counts. Bare numeric IDs inside JSON are not treated as TCKN.
- 03
EDM
Exact data match: hashed columns of your customer table; the raw records never reach the agent or the console.
- 04
Fingerprint
Document fingerprinting; catches partial copies and reformatted versions.
- 05
Machine learning and OCR
Embedded OCR for text inside images and a gradient-boosted model that suppresses false positives; both run on the endpoint.
Two appliances, three agents, a one-way control channel
The management appliance hosts the console, the APIs and the data stores. The Network DLP proxy is a separate box and is the only one that connects to management. Endpoints send heartbeats to management over 443; management never connects to them.
Network DLP proxy appliance
- Forward proxy :8080
- TLS inspection (own CA + CRL)
- Content rules · OCR
- Web categories
- PAC/WPAD :80
443 · one way
Management appliance
- Console · Cloud API
- PostgreSQL · Redis
- Policy and rule store
- Incidents · discovery · CASB · ML
443 · one way
Endpoints
- Windows · Linux · macOS agent
- User window
- Browser extension
- Office add-in
Measurements, not marketing
Scenarios run end to end in October 2026 against a real Active Directory environment (Samba DC, Windows Server 2022 RDS, Ubuntu 24.04).
Multi-session identity
Two users exfiltrated data at the same time on one RDS host; each incident was attributed to the right user and session.
Agentless Kerberos
The domain-joined proxy authenticated the user with 407 Negotiate and blocked a TCKN upload, recorded under the user name.
Linux transparent steering
A command-line tool with no proxy settings was redirected through nftables and stopped by policy.
Penetration test
No identity spoofing, no open relay, no cross-tenant access; the one reflected XSS found was fixed the same day.
Two ISOs, no internet required
The management appliance and the Network DLP proxy install from separate ISOs; images and agent packages are inside. The proxy connects to management one way only; you never open a rule from the management appliance into your network.
- Unattended Ubuntu 24.04 LTS install, signed Docker images loaded at first boot
- Agent or agentless (AD) mode chosen in the proxy ISO boot menu
- Console-generated MSI and Linux packages with enrolment tokens; heartbeat every 15 seconds
- Central, ring-based staged agent updates with sha256 verification and automatic rollback
See it in your own environment
With the installation guide, port matrix and AV/EDR exclusion list you can stand up a PoC in an afternoon. The 30-day trial licence works offline.